Sooner or later, most organisations face a serious cyber incident, and what happens in the first hour often decides the outcome. Without a clear escalation plan or an external team on call, every minute of delay compounds the financial loss, slows recovery, and increases your exposure under GDPR, DORA and NIS2. Monitoring just tells you something happened; it doesn’t actively respond to it, and that gap is where the real damage happens.
Your concerns, our answers
We’ve been hit by ransomware. Who do I call now?
Retainer customers can reach a live person on our 24/7 hotline within 30 minutes, and we open an incident management case within an hour.
Should I pay the ransom, or negotiate with the attackers?
We do not negotiate with attackers ourselves, in line with FIRST.org guidance. We help you assess your options and, if needed, bring in a trusted specialist partner who can handle negotiations within the legal framework, including sanctions screening.
We already have monitoring in place, isn’t that enough?
Monitoring alerts you to an incident; it doesn’t contain or investigate it. Our DFIR experts do both. Under NIS2, you must send an early warning within 24 hours, and we help you draft that initial report, as well as your notifications under GDPR and DORA.
You have cyber insurance and monitoring in place. But what happens when an incident strikes?
One of only 10 FIRST-accredited CSIRT’s in Belgium: peer-audited, with global threat-intelligence sharing.
For retainer customers: a 24/7 hotline with documented SLAs, including human response within 30 minutes, an incident management meeting within an hour, and on-site support in Belgium within 4 hours.
Technical investigation and GDPR/DORA/NIS2 breach-management expertise from one team, not stitched together from two separate providers.
Already run an internal SOC? We act as your Tier 3 escalation and forensic surge capacity, so you don’t have to do it yourself.
Readiness assessments, response playbooks and clear escalation contacts, backed by monthly reviews with a dedicated delivery manager, so you’re fully prepared when an incident occurs.
No incident response agreement in place? We can still respond to an active incident on a time-and-materials basis, with hours agreed and tracked throughout the investigation.
In-depth forensic investigation, malware analysis and attack-timeline reconstruction, including support for legal, insurance or litigation proceedings.
Breach qualification, risk assessment and support preparing your notification to the data protection authority, coordinated with your DPO and legal advisors.
With an incident response retainer, a live person answers your call within 30 minutes and we hold a remote incident management meeting within about an hour. From there, we work in parallel on containment, investigation and your regulatory notification obligations. If the situation demands it, on-site support in Belgium follows within 4 hours.
Do I need a retainer in place before you can help?
No. We can respond to an active incident on an ad-hoc basis without a retainer. A retainer gets you a documented SLA, readiness playbooks and an agreed upon contact list before a crisis, rather than during one, when each second counts.
Do you handle the GDPR breach notification for us?
We support you throughout: qualifying the breach, assessing the risk, and preparing what you need to notify the data protection authority within the legal deadline. The final notification decision and liability remain yours. Not sure where your organisation stands on GDPR or NIS2? See our GRC page.
What if we don’t already have logging or monitoring in place?
We can still help, but forensic depth entirely depends on visibility: without basic endpoint and network logs, we can usually confirm that an active incident occurred, but tracing its full root cause and blast radius becomes severely limited. However, our SOC or a readiness assessment can help close that gap.
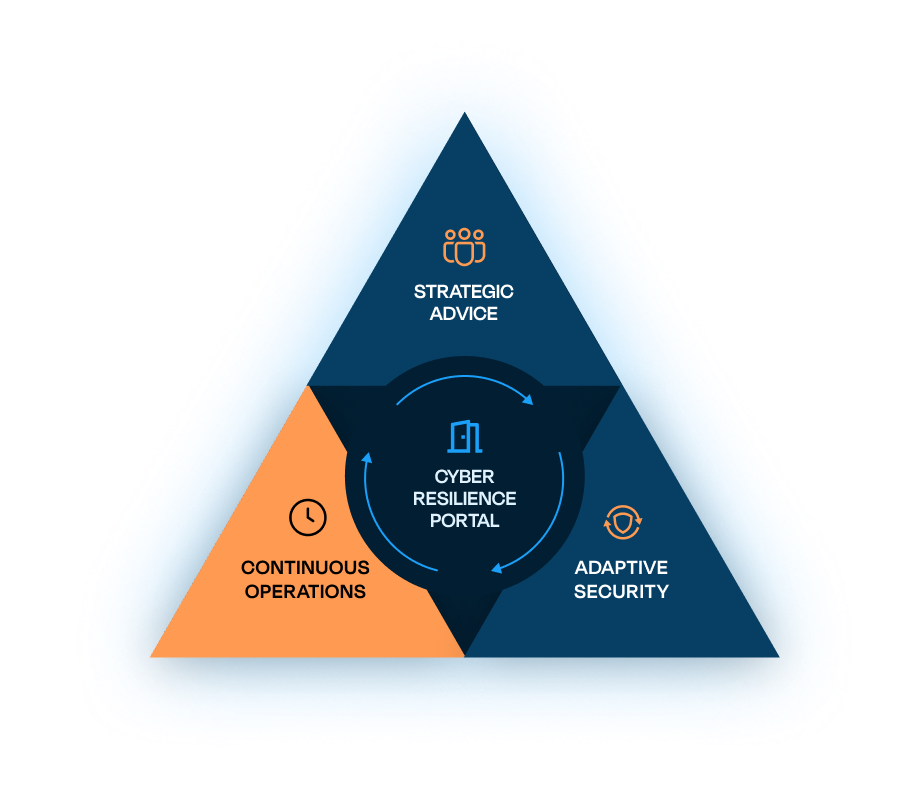
The Triangle of Cyber Resilience
Digital Forensics & Incident Response (DFIR) is part of Continuous Operations, Approach Cyber’s pillar for ongoing vigilance and validation, alongside our SOC, Phishing & Awareness, Vulnerability & Exposure Management, Managed Firewall Services and Offensive Security teams. Continuous Operations validates, in real time, what Strategic Advice designed and Adaptive Security enforced.