
Offline, or protected? It did not have to be that way. A Web Application Firewall can step in exactly where PHP2Shell strikes. But having a WAF is not the same as being protected: the difference lies in how it is tuned. What you will find in the advisory How the attack works, and why […]

What happened On 21 October 2026, PHP released fixes for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619. They allow remote code execution without a login and carry a CVSS v4.0 score of 9.2. According to PHP, all installations serving web requests are affected, including PHP-FPM, Apache mod_php and php-cgi. The fixes are in versions 8.5.12, 8.4.27, […]

CRA reporting obligations started earlier than many organisations expected. Since 11 September 2026, manufacturers of in-scope products with digital elements need to be able to report actively exploited vulnerabilities and severe product-security incidents to ENISA and the designated CSIRT coordinator, such as the CCB in Belgium. For many organisations, December 2027 has become the date […]
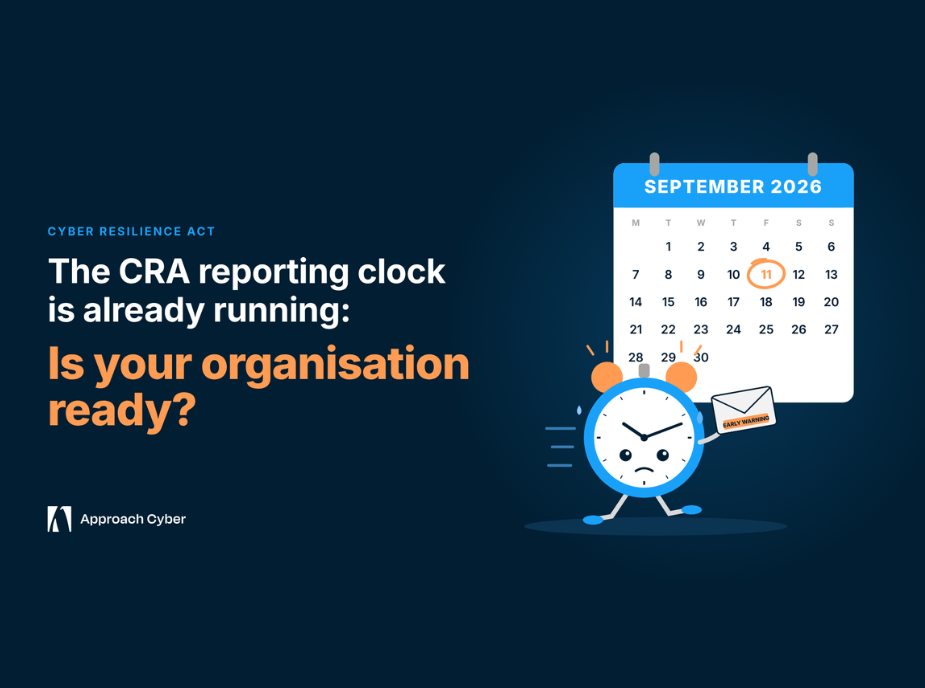
For many organisations, the CRA is still associated with December 2027. That is when the regulation becomes broadly applicable to products with digital elements placed on the EU market. But the first operational obligations arrived earlier, and they are already in force. Why does 11 September 2026 matter more than December 2027? The July […]

At AXS Guard by Approach Cyber, we believe that effective perimeter security begins with the core architecture of the product itself. An incident like this serves as a critical reminder of the importance of a Zero Trust approach and strict management of administrative environments. How AXS Guard inherently prevents these risks: No public access to management functions by default: The AXS Guard management platform is not accessible directly from the public internet via simple IP addresses using default credentials. Administrative access requires strict authentication paths. Mandatory Multi-Factor Authentication (MFA):
In an increasingly unpredictable digital world, prevention alone is no longer enough. We are your local and pragmatic cyber security partner delivering complete cyber resilience, to bring you digital peace of mind.
Three Pillars. One Resilient Business.
Strategic Advice sets the direction and helps you make informed security decisions. Adaptive Security puts that strategy into practice, powered by our sovereign AXS Guard platform. Continuous Operations keep your defences effective and validate your resilience every day. Each pillar delivers value on its own. Together, they provide a comprehensive approach to cyber resilience.

At Approach Cyber, we believe everyone deserves digital peace of mind. Inspired by the vision, our mission is to protect our clients’ digital assets, allowing them to focus on what matters most—their business.
Our purpose is to deliver cyber serenity to society empowering individuals and organisations to navigate the digital world with confidence and trust. If you share our commitment to secure the digital future, we invite you to explore our career opportunities today.